Infographic
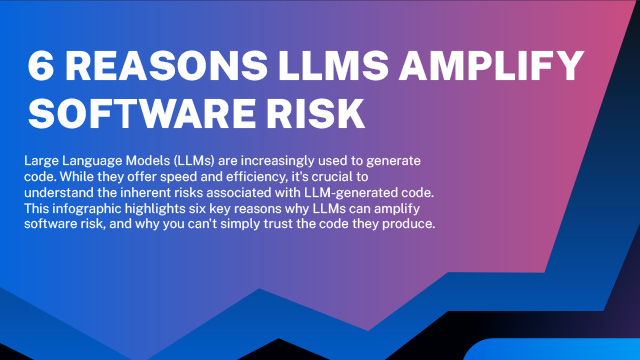
Large language models write code fast, and that speed makes it tempting to trust what they produce. This one-page infographic sets out six reasons not to. LLMs are trained on public codebases that include flawed security patterns. They aim for code that runs rather than code that is safe. Without explicit security instructions in the prompt, they will not enforce best practices. Secure coding differs from one language to another, but models apply patterns inconsistently. They have no feedback loop, so they never test or improve based on security outcomes. And because the output looks clean, it creates a false sense of safety that can mask hidden vulnerabilities. Together, the six points make a quick case for treating AI-generated code as untrusted until it has been scanned and reviewed, however polished it looks.
Download this Infographic
Enter your work email address to access the full document at no cost.
Please enter a valid email address.
By downloading you agree to Veracode’s Privacy Policy and IT eBulletins Privacy Policy. IT eBulletins may share your contact information with Veracode.